
CISA, the Federal Bureau of Investigation (FBI), and the Australian Cyber Security Centre (ACSC) have released a joint Cybersecurity Advisory (CSA) with known BianLian ransomware and data extortion group technical details. Microsoft and Sophos contributed to the advisory.
To reduce the likelihood and impact of BianLian and other ransomware incidents, CISA encourages organizations to implement mitigations recommended in this advisory. Mitigations align with the Cross-Sector Cybersecurity Performance Goals (CPGs) developed by CISA and the National Institute of Standards and Technology (NIST).
This joint CSA is part of CISA’s ongoing #StopRansomware effort.
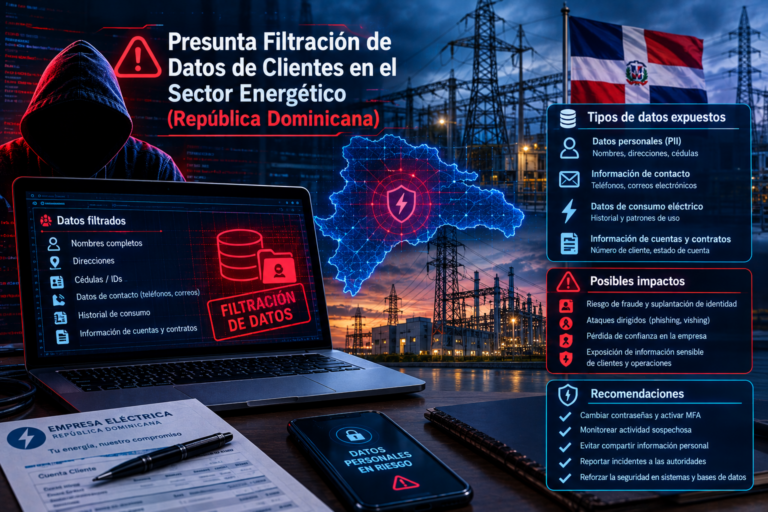
Presunta Filtración de Datos de Clientes en el Sector Energético (República Dominicana)
El 30 de octubre de 2026, la inteligencia de fuentes abiertas identificó que un actor de amenazas bajo el seudónimo “K3RN3L_P4N1C” anunció en un foro